
Unit of the Exchange Kraken, engaging in security research, Passed the analysis of the vulnerabilities of the popular model of the Batmtwo cryptomat from General Bytes.
According to article
on the Kraken Security Labs blog, The widely used cryptomate model has several software and hardware vulnerability. 20 April Kraken research unit notified the manufacturer of cryptomats company General Bytes about attack vectors. General Bytes released corrections for the server system, However, some corrections may require finalization of equipment.
According to Kraken security researchers, The Batmtwo model under consideration (GBBATM2) had several vulnerabilities, including problems with the default administrator QR code, basic Android operating software, Cryptomat control system and hardware case of the device.
Problems with the administrator QR code
When purchasing the GBBATM2 cryptomate, its new owner must configure the device using the QR code of the “Administration Key”, which must be scanned on cryptomat. QR code, containing password, It is necessary to install separately for each ATM in the BECENT system.
However, when viewing the administrator interface code, Kraken's researchers discovered, that it contains a hash of the control key of factory settings by default. Kraken has acquired several former cryptomats from different sources and found out, that each of them has the same configuration of keys by default. It means, that many GBBATM2 owners did not change the administrator's QR code. During testing, there was no possibility of managing the administration key for a group of cryptomats, That is, each QR code had to be changed manually. In this way, Anyone can take control of the cryptomat through an administrative interface, Just changing the address of the device control server.
Hardware
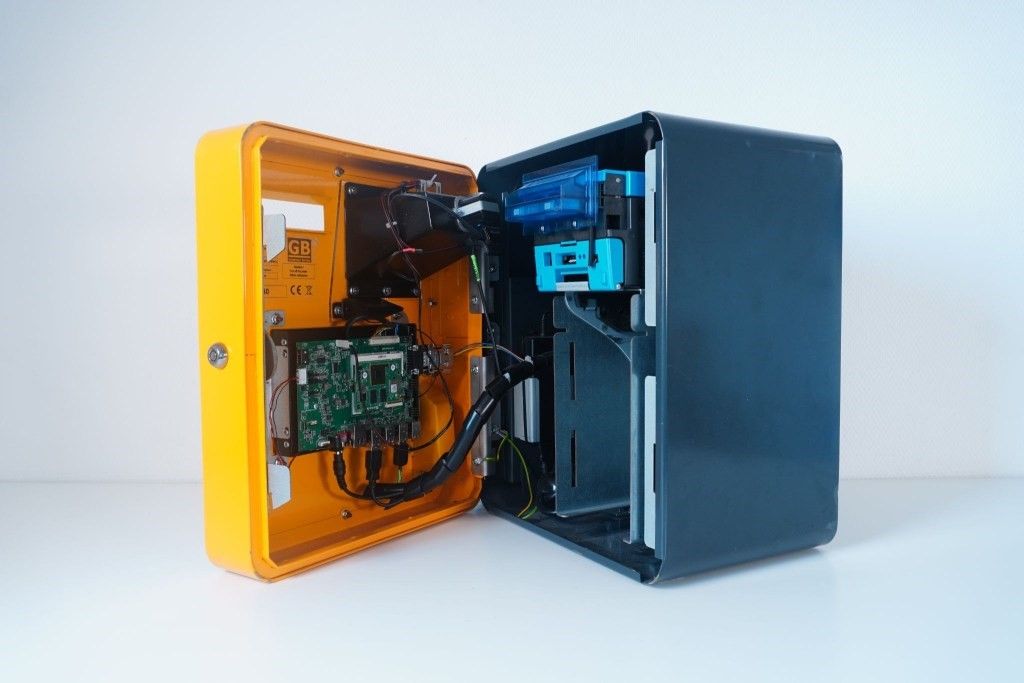
GBBATM2 has one compartment, which is protected by one castle. Its autopsy provides direct access to all the internal components of the device. The device does not contain local or server alarm, warning others about that, that the internal compartment was opened. At this stage, a potential attacker can hack a cash box, Built -in computer, Webcam and fingerprint scanner.
Software
According to the researchers, There are no many general security functions in the Android Batmtwo operating system. When connecting a USB-keyboard to BATM, you can get direct access to a full user interface Android interface, which allows anyone to install applications, Copy files or perform other malicious actions, eg, send closed keys to the attacker.
Android supports the "Self -Service terminal", which blocks the user interface in one application, what can prevent access to other software areas, However, it was not included in the cryptomat system.
Lack of firmware checks/software
Batmtwo contains a built -in computer based on NXP I.MX6. Researchers Kraken discovered, that Batmtwo does not use the function of safe processor loading and that it can be reprogrammed, Just by connecting a USB cable to the port on the payroll and turning on the computer, Holding the pressed button.
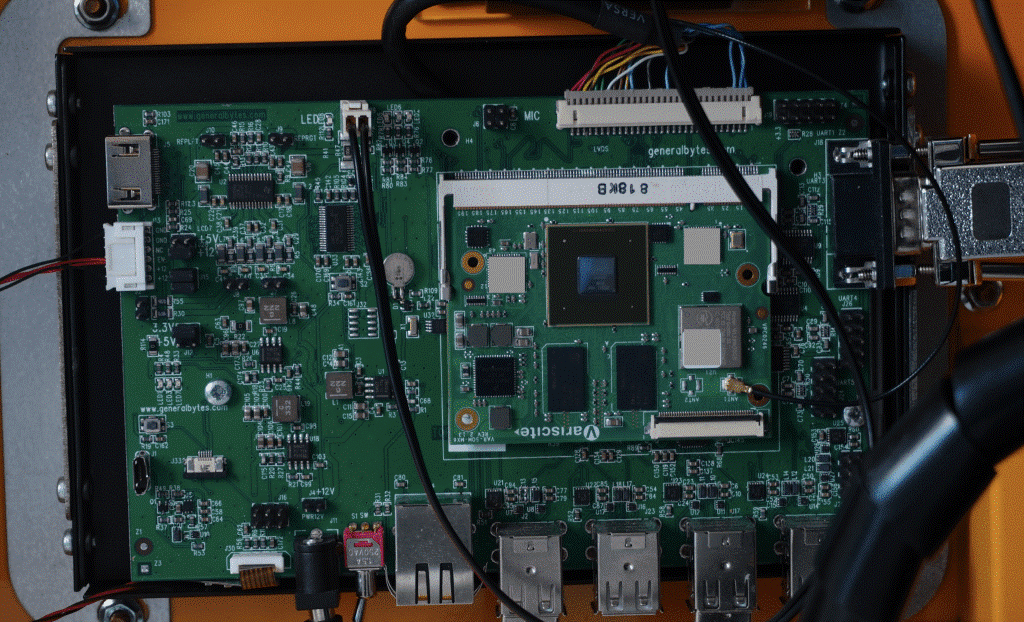
Built -in computer in Batmtwo: SOM VARISCITE I.MX6 with a non-standard booster board.
Besides, The device bootloader is unlocked: Simple connection of the sequential adapter to the UART port on the device is enough to obtain privileged access to the bootloader. Researchers note, that the process of safe loading of many I.MX6 processors is vulnerable
For attack, However, there are newer processors with corrected vulnerability on the market, however, they can be inaccessible due to global lack of chips.
Lack of protection against falsification of intersyite queries in the server part of the ATM
Batm cryptomats are controlled using Crypto Application Server (CAS) – software, which can be placed by the operator or licensed as SaAS. The Kraken team discovered, that CAS does not implement any means of protection against falsification of intersight queries, which allows the attacker to generate authenticated requests for CAS. Although most of the endpoints are protected very difficult to guessed identifiers, Researchers were able to identify several CSRF vectors, which can successfully compromise CAS.
In conclusion, the researchers noted, that the safety of BATM cryptomats remains in question due to well-known vulnerabilities as in their hardware, and in the software. Kraken Security Labs recommends using only Batmtwo cryptomats, installed in reliable places.
According to Coin Atm Radar, General Bytes – The second largest manufacturer of cryptomats, which is 22.7% world market. Recall, that in July the total number of established cryptomats in the world exceeded
24 000.